Accessibility links
  • Skip to main content
News Icon NEWS FILTER
All News Scams & Phishing Your Security Mobile Security Identity Theft Corporate Security Security Education Videos
Search Icon SEARCH
 

Email Icon SUBSCRIBE TO WEEKLY NEWSLETTER
The Reality Of Growing ATO Cross-Platform Attacks
Facebook   X   LinkedIn   Email

The Reality Of Growing ATO Cross-Platform Attacks

February 26, 2026

Just the thought of an account takeover (ATO) sends shivers down the spines of system administrators. Organizations are highly vulnerable to these attacks, and the reality is just last year, 83% have experienced an ATO. The damage done by these security breaches is harmful enough, but when they lead to cross-platform attacks, it’s a security red alert for system admins and the organizations they protect.

When ATO’s = Cross Platform Attacks

Some organizations encountered ATO’s over 10 times and 70% of security leaders report them as their biggest worry—even more than ransomware. More often, email phishing was the likely source of an ATO, but now, cloud security is increasingly targeted. As these cloud ecosystems integrate and proliferate, so do opportunities for cross-platform compromise. With increased cloud entry points, each opening provides its own unique risk for an organization’s security across multiple platforms.
Cross-platform attacks have numerous benefits for attackers since once inside a system, they can move across multiple cloud-connected platforms and apps. The more these things are integrated, the more opportunities they provide to do substantial damage to an organization. Data theft, company downtime, financial loss, customer compromise, and reputational damage—it’s all possible with cross-platform attacks. The question now becomes, can an organization survive such an attack?

Notorious Cross-Platform Attacks

The SolarWinds attack grabbed headlines as one of the most devastating cyberattacks to date. Russian nation-state actors breached a SolarWinds supplier, unfolding a cross-platform nightmare against their network and customers. Over 18,000 clients were breached, including several U.S. government agencies. Some breached companies reported their own customers were also affected.

A compromised password led to a devastating cyberattack against Colonial Pipeline, a major U.S. fuel supplier. Russia’s DarkSide threat actors got to work breaching cross-platform IT infrastructure. The attack forced Colonial to shut down 5,500 miles of pipeline in response to DarkSide’s ransomware attack. Gasoline, jet fuel, and diesel distribution were halted along the U.S. northeast until Colonial ultimately paid the $4.4 million ransom demand.

It seems cross-platform cyberattacks via ATO’s are here to stay for now. One component giving them a foothold is the human element. Employees lacking cyber-education unknowingly assist with ATO’s. Add to that, growing cloud-connections creating cross-platforms within industries, and it’s a dangerous concoction in search of a remedy. Let’s hope security pros find it.
Account Takeover Fraud Steals Your Identity, Money, And More

Identity Theft

Account Takeover Fraud Steals Your Identity, Money, And More

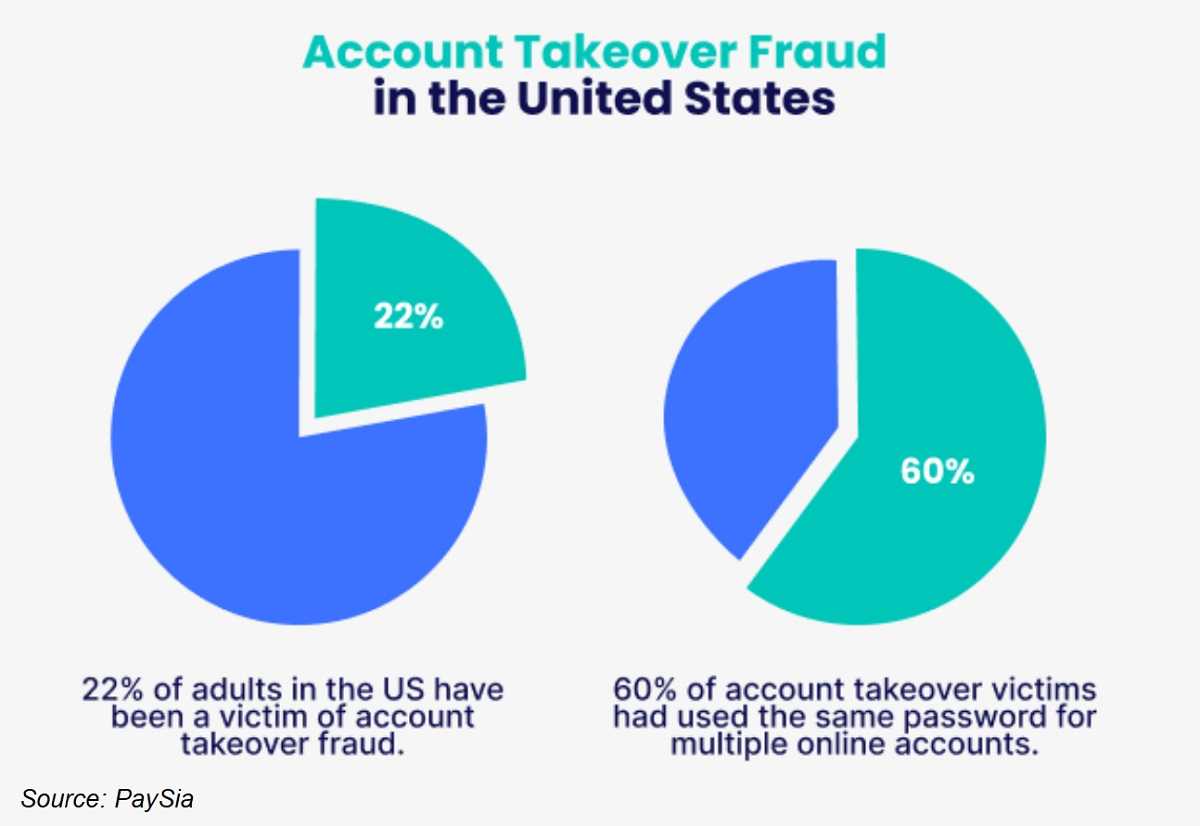
With a significant swell in the number of those working from home, come the most historic levels of hacking the world has ever seen. Account takeover (ATO) fraud attacks have been growing yearly, accounting for much of the identity fraud-based financial losses to consumers and businesses. ATO fraud can lead to empty bank accounts and damaged reputations, and those recovering from an attack find it’s an expensive, time consuming, and frustrating task. READ FULL STORY

Account Hijacking – Keep Yours From Cyberthieves

Your Security

Account Hijacking – Keep Yours From Cyberthieves

Most of us would agree there are too many ways our sensitive PII ends up in the hands of cybercriminals. One of these ways is account hijacking and few users, if any, are spared from this cyberthreat. This type of identity theft can happen without us knowing until it’s too late, but we can help prevent it. A closer look at this all-too-common cybercrime, also called account takeover, can help to make us cyber-smarter and our accounts and PII safer. READ FULL STORY

Attackers Target Neglected Websites to Go Phishing

Scams & Phishing

Attackers Target Neglected Websites to Go Phishing

According to a recent study by Kaspersky, there is a growing trend of attackers focusing on abandoned and minimally maintained websites for the purpose of hosting very legitimate-looking phishing pages. In fact, the research revealed a significant volume of compromised websites. Between mid-May and the end of July, it identified 22,400 distinct WordPress websites that had been compromised by threat actors to serve as platforms for hosting phishing pages. READ FULL STORY


Close
Fraud News & Alerts!

Keep up with the latest cyber security news through our weekly Fraud News & Alerts updates. Each week you will receive an email containing the latest cyber security news, tips and breach notifications.


You're all set!

You will receive your first official security update email within the next week.

A welcome email has also just been sent to you. If you do not receive this email within the next few minutes, please check your Junk box or spam filter to confirm our emails are not being blocked.


Help  
Enter any word or words you like.        

The email newsletter will arrive from news@stickleyonsecurity.com


Loading
Please wait...